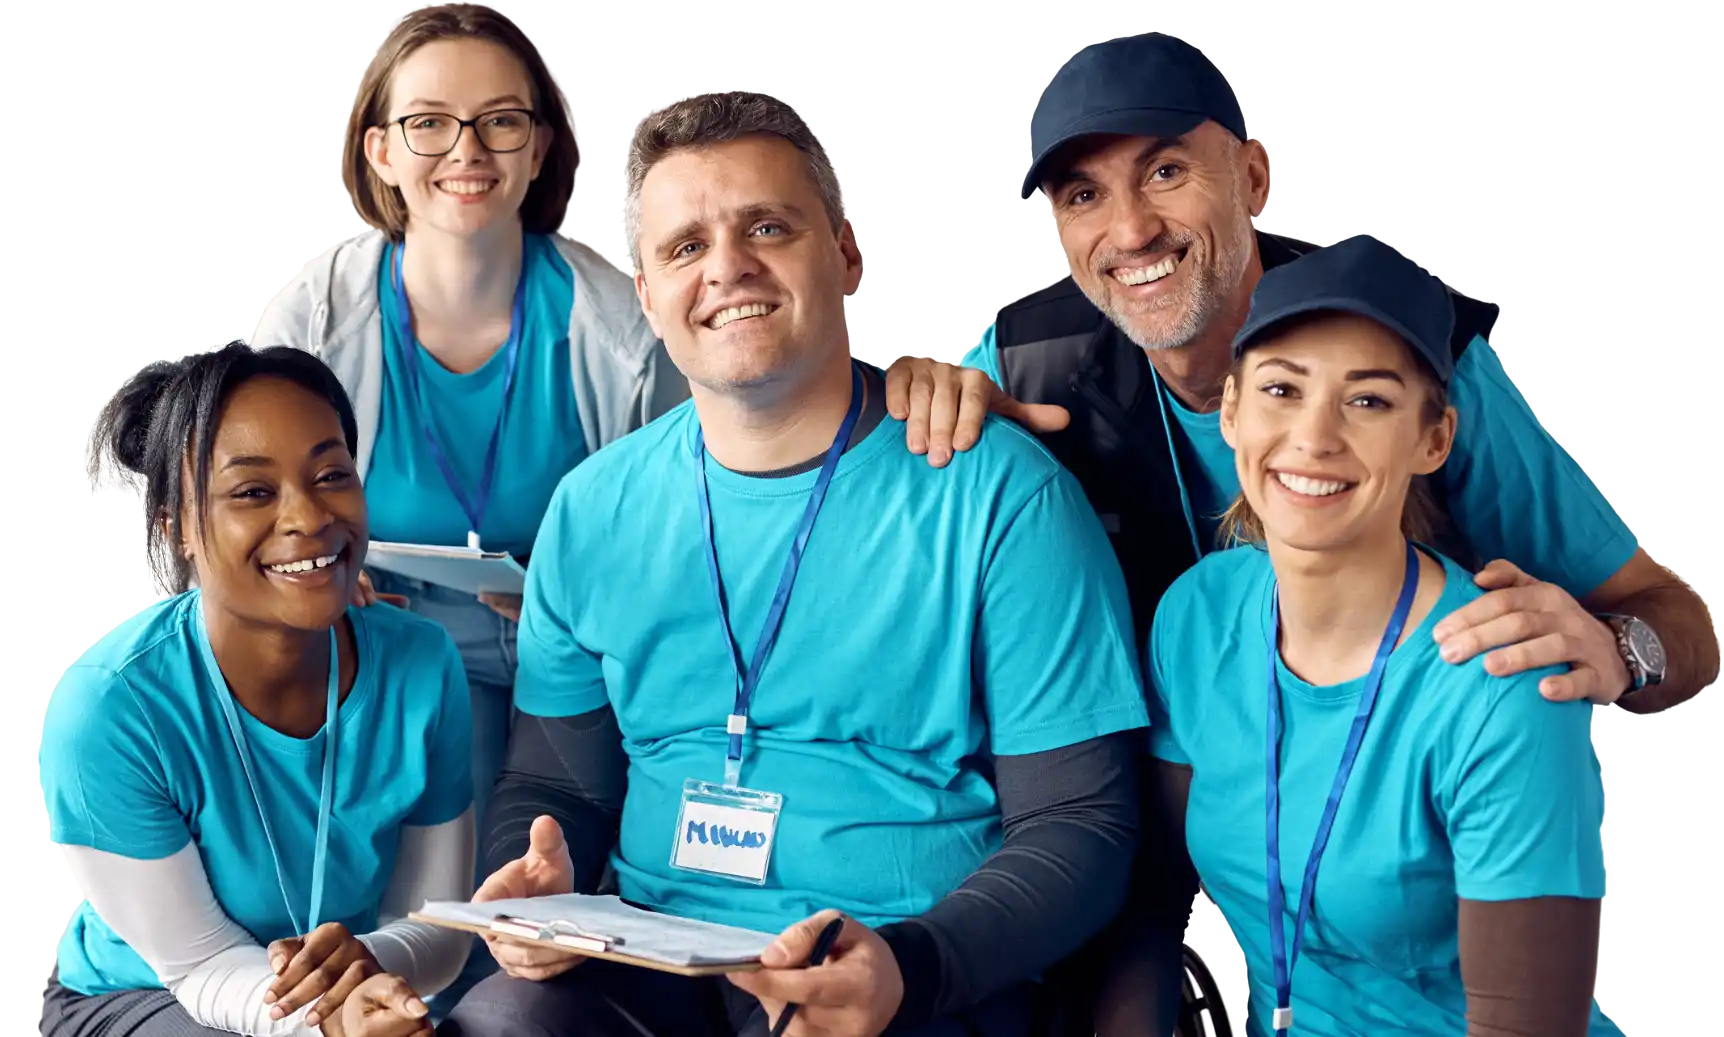
The Process Behind Every Organization We Support
Every engagement starts with an honest look at where you stand, moves into a plan ranked by what matters most to your board and your budget, and stays in place well past the day the work gets done. This is what Secure Assess looks like at every stage.
“An indispensable partner and a trusted provider for our organization.”
Karen Smizer | Director of Philanthropy, South Shore Stars
An Assessment Process Built Around What Nonprofits Need
Every organization we work with wants the same things from a Secure Assess engagement, clarity, prioritization, a practical roadmap, and decisions their board can stand behind. These are the needs that shape how we built our process.
Clarity on Exactly Where You Stand
You want an honest, documented picture of your security and technology today, ranked by what matters most to your board.
Recommendations Ranked by What Matters Most
You want your findings prioritized against your board’s priorities and your budget, so the most urgent gaps get addressed first.
A Roadmap With Real Costs and Timelines Attached
You want a practical roadmap with clear actions, costs, and timelines behind every recommendation, not just a list of findings with nowhere to go next.
Decisions Your Board Can Stand Behind
You want your leadership and board making technology decisions with confidence, backed by someone who can walk them through exactly why.
The Method Behind Every Assessment We Run
Every assessment follows the same five-step process, so you always know what to expect and why a recommendation made the list.
Every Engagement Starts With Discovery
We take time to understand your organization’s mission and goals before we evaluate a single system.
Evaluated Against the Pillars That Matter Most
Your organization gets measured against the same categories every time, tailored to whichever assessment fits your need.
Findings Turned Into a Score Your Board Understands
We turn what we find into a clear maturity score and plain-language insights, so leadership knows exactly where things stand.
Every Recommendation Ranked by What Matters Most
We identify the opportunities with the biggest impact first, so your team always knows what to tackle next.
A Roadmap Built for Lasting Impact
You get a clear roadmap that turns priorities into lasting progress toward your mission.
“They’re so accessible and able to troubleshoot our IT issues, typically resolving problems within an hour – same-day solutions we’ve never experienced with any other provider.”
Jennifer Matthews | Executive Director
L’Arche
The Assessments Behind Every Recommendation We Make
Depending on where your organization needs the clearest picture, an engagement typically draws from the following, backed by engineers who carry CISA and CISSP certifications on every assessment.
Technology Assessment
A full view of your technology environment, covering cybersecurity and operational readiness, prioritized for board-level decision-making.
Security and Vulnerability Assessment
A clear look at where your organization is exposed, so leadership can reduce risk before someone else finds the gap.
AI Readiness Assessment
An understanding of where AI is already in use across your organization, paired with a roadmap for secure, responsible adoption.
Data Intelligence Assessment
A look at how information moves across your organization’s programs and departments, breaking down the silos that keep valuable data from working together.
Google Workspace Assessment
A review of your Google Workspace security and governance, identifying ways to strengthen protection without slowing your team down.
Microsoft 365 Assessment
A review of your Microsoft 365 tenant, identifying security gaps and configuration risks across the tools your team relies on daily.
Ongoing Remediation, Management, and Reporting
Fixes get made and tested, then stay under regular review and monitoring, with straight answers ready whenever your board asks how things are going.
FAQs
A few of the questions we hear most often about Secure Assess. If yours is not here, send it over and we will get you a direct answer.
How long does an assessment take to complete?
Timelines vary by assessment type and the size of your organization, and we’ll confirm a specific timeline once we understand your scope during the initial discovery conversation.
Do we have to commit to remediation work to get an assessment?
No. Many organizations start with an assessment on its own to understand where they stand, and decide on remediation once they’ve seen the findings and the ranked recommendations.
What happens after the assessment is complete?
You get a documented report with a maturity score and prioritized recommendations, along with a roadmap for what to tackle first if you choose to move into remediation.
Can you tell us which assessment we need, or do we choose?
We’ll help you land on the right starting point during an initial conversation about your goals, rather than asking you to guess from a list on your own.
Ready to Build Your Success Plan?
Let’s start with your goals.
Whether you’re weighing next year’s technology roadmap or signing off on the budget behind it, a first conversation with our team starts with your goals and your constraints.
- We start with a conversation about your goals and your risks.
- We ask questions before we make recommendations.
- You’ll walk away with a clear next step within 30 minutes.